


Quality D-CSF-SC-23 PDF Dumps - D-CSF-SC-23 Exam Questions
Most UptoDate EMC D-CSF-SC-23 Exam Dumps PDF 2024
EMC D-CSF-SC-23 exam covers a range of topics related to the NIST Cybersecurity Framework. These include the five functions of the framework: identify, protect, detect, respond, and recover. Candidates are expected to have a deep understanding of each of these functions, as well as the subcategories and implementation tiers that are associated with them. D-CSF-SC-23 exam also covers topics such as risk management, threat intelligence, and incident response.
EMC D-CSF-SC-23 (NIST Cybersecurity Framework 2023) Certification Exam covers a wide range of topics related to cybersecurity risk management and compliance, including risk assessment, risk management, incident response, and compliance with regulatory requirements. D-CSF-SC-23 exam is designed to test the knowledge and skills of professionals who work in various roles, such as cybersecurity analysts, cybersecurity managers, compliance officers, and risk managers. D-CSF-SC-23 exam is also designed to validate the knowledge and skills of professionals who work in various industries, such as healthcare, finance, and government.
NEW QUESTION # 27
What is a consideration when performing data collection in Information Security Continuous Monitoring?
- A. Data is best captured as it traverses the network.
- B. Data collection efficiency is increased through automation.
- C. The more data collected, the better chances to catch an anomaly.
- D. Collection is used only for compliance requirements.
Answer: B
NEW QUESTION # 28
A CISO is looking for a solution to lower costs, enhance overall efficiency, and improve the reliability of monitoring security related information.
Which ISCM feature is recommended?
- A. Provisioning
- B. Reporting
- C. Automation
- D. Collection
Answer: C
NEW QUESTION # 29
The network security team in your company has discovered a threat that leaked partial data on a compromised file server that handles sensitive information. Containment must be initiated and addresses by the CSIRT. Service disruption is not a concern because this server is used only to store files and does not hold any critical workload.
Your company security policy required that all forensic information must be preserved.
Which actions should you take to stop data leakage and comply with requirements of the company security policy?
- A. Create a firewall rule to block all external connections for this file server and keep it powered on for further analysis.
- B. Restart the server to purge all malicious connections and keep it powered on for further analysis.
- C. Disconnect the file server from the network to stop data leakage and keep it powered on for further analysis.
- D. Shut down the server to stop the data leakage and power it up only for further forensic analysis.
Answer: C
NEW QUESTION # 30
What contains a predefined set of efforts that describes an organization's mission/business critical processes, and defines how they will be sustained during and after a significant disruption?
- A. Disaster Recovery Plan
- B. Risk Assessment Strategy
- C. Business Impact Analysis
- D. Business Continuity Plan
Answer: D
NEW QUESTION # 31
Which category addresses the detection of unauthorized code in software?
- A. PR.AT
- B. PR.DS
- C. DE.CM
- D. DE.DP
Answer: C
NEW QUESTION # 32
Match the security event to its description.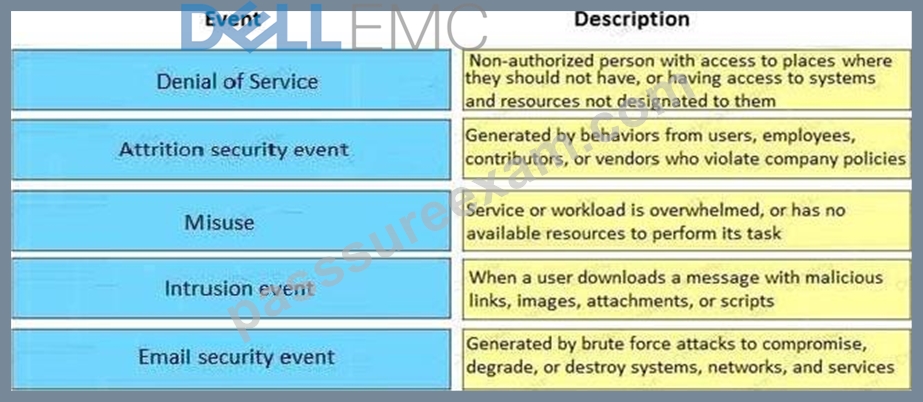
Answer:
Explanation: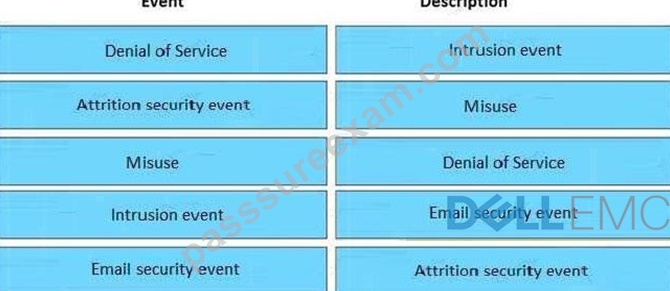
NEW QUESTION # 33
What is the main goal of a gap analysis in the Identify function?
- A. Determine actions required to get from the current profile state to the target profile state
- B. Identify gaps between Cybersecurity Framework and Cyber Resilient Lifecycle pertaining to that function
- C. Identify business process gaps to improve business efficiency
- D. Determine security controls to improve security measures
Answer: A
NEW QUESTION # 34
What should be inventoried within an organization using an asset inventory software application?
- A. Data, devices, software, and audit logs
- B. Data, devices, identities, and software
- C. Data, personas, identities, and CMDB
- D. Data, profiles, software, and system logs
Answer: B
NEW QUESTION # 35
The warranty on your organization's air conditioning system has expired. No alert was sent to anyone within the organization. During an extended number of days of record heat, the air conditioning units fail.
However, maintenance personnel will not work on non-warrantied systems.
Failing to catalog warranty information about the air conditioning units is a failure in which function?
- A. Detect
- B. Identify
- C. Protect
- D. Recover
Answer: B
NEW QUESTION # 36
What is part of the Pre-Recovery phase?
- A. Backup validation
- B. Restore assets
- C. Validate functionality
- D. Monitor assets
Answer: C
NEW QUESTION # 37
The Disaster Recovery Plan must document what effort in order to address unrecoverable assets?
- A. RTO savings
- B. Recovery resources
- C. Recovery priority
- D. Recovery resources
Answer: C
NEW QUESTION # 38
What is an accurate statement concerning the Cyber Resilient Lifecycle (CRLC) and the Cybersecurity Framework (CSF)?
- A. The CRLC is focused on cybersecurity; the CSF is focused on science and technology.
- B. The CRLC can be used to make the CSF actionable.
- C. The CRLC and CSF are separate frameworks, and are used separately.
- D. The CRLC is focused on business resiliency; the CSF is focused on providing a framework.
Answer: B
NEW QUESTION # 39
Rank order the relative severity of impact to an organization of each plan, where "1" signifies the most impact and "4" signifies the least impact.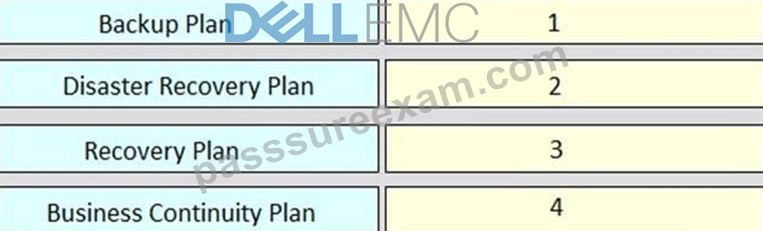
Answer:
Explanation: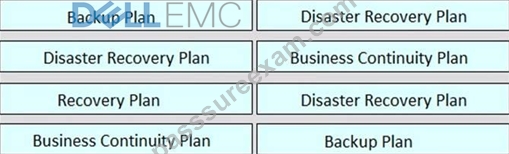
NEW QUESTION # 40
What is highlighted by the Cyber Resilient Lifecycle?
- A. Disaster Recovery Plan
- B. Incident Response Plan
- C. Business Intelligence Analysis
- D. Security Reference Architecture
Answer: B
NEW QUESTION # 41
Which mechanism within the NIST Cybersecurity Framework describes a method to capture the current state and define the target state for understanding gaps, exposure, and prioritize changes to mitigate risk?
- A. Functions
- B. Categories
- C. Tiers
- D. Profiles
Answer: C
NEW QUESTION # 42
What is concerned with availability, reliability, and recoverability of business processes and functions?
- A. Disaster Recovery Plan
- B. Recovery Strategy
- C. Business Impact Analysis
- D. Business Continuity Plan
Answer: D
NEW QUESTION # 43
What is considered outside the scope of a BIA?
- A. Estimated probability of the identified threats actually occurring
- B. Selection of full, incremental, or differential backups
- C. Determination of capacity requirements for backups
- D. Efficiency and effectiveness of existing risk mitigation controls
Answer: B
NEW QUESTION # 44
What could be considered a set of cybersecurity activities, desired outcomes, and applicable references that are common across critical infrastructure sectors and align to five concurrent and continuous functions?
- A. Profile
- B. Baseline
- C. Governance
- D. Core
Answer: D
NEW QUESTION # 45
A security audit of the systems on a network must be performed to determine their compliance with security policies.
Which control should be used for the audit?
- A. DE.CM
- B. RS.MI
- C. PR.DS
- D. ID.AM
Answer: C
NEW QUESTION # 46
You have been tasked with documenting mission critical procedures of an organization that need to be sustained through a significant disruption.
What document would you develop?
- A. Business Impact Assessment
- B. Risk Analysis Report
- C. Regression Test Plan
- D. Business Continuity Plan
Answer: D
NEW QUESTION # 47
A bank has been alerted to a breach of its reconciliation systems. The notification came from the cybercriminals claiming responsibility in an email to the CEO. The CEO has alerted the company CSIRT.
What does the Communication Plan for the IRP specifically guide against?
- A. Accelerated turn over
- B. Transfer of chain of custody
- C. Rushed disclosure
- D. Initiating kill chain
Answer: C
NEW QUESTION # 48
In which function is the SDLC implemented?
- A. Detect
- B. Protect
- C. Respond
- D. Recover
Answer: C
NEW QUESTION # 49
Which NIST Cybersecurity Framework component defines activities and references for a specific cybersecurity approach?
- A. Core
- B. Tiers
- C. Profile
- D. Category
Answer: C
NEW QUESTION # 50
Consider the following situation:
- A complete service outage has occurred, affecting critical services
- Users are unable to perform their tasks
- Customers are unable to conduct business
- Financial impact is beyond the highest allowed threshold
What is the correct classification level for this situation?
- A. High impact
- B. Safety critical
- C. Mission critical
- D. Business critical
Answer: C
NEW QUESTION # 51
......
EMC D-CSF-SC-23 (NIST Cybersecurity Framework 2023) Exam is a highly respected certification in the field of cybersecurity. D-CSF-SC-23 exam is designed for professionals who are looking to enhance their skills and knowledge in the cybersecurity domain. D-CSF-SC-23 exam is developed by the National Institute of Standards and Technology (NIST) and is recognized worldwide.
100% Free Dell Security D-CSF-SC-23 Dumps PDF Demo Cert Guide Cover: https://actualtests.passsureexam.com/D-CSF-SC-23-pass4sure-exam-dumps.html